Available either online or on-site, these instructor-led live OWASP (Open Web Application Security Project) training courses utilize interactive discussions and hands-on exercises to illustrate how to protect web applications and services using the OWASP testing framework.
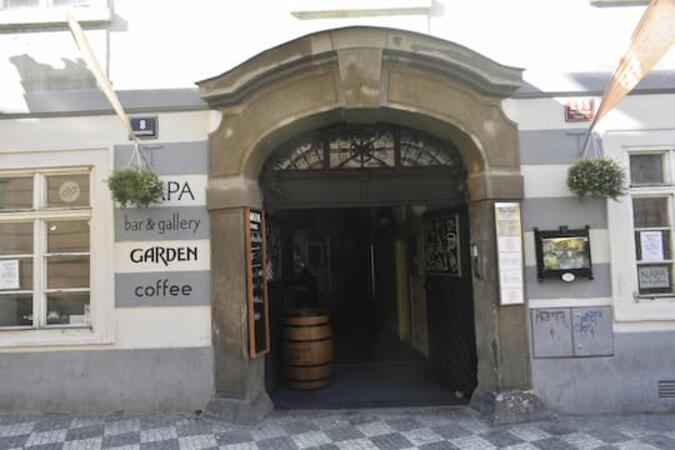
OWASP training is offered as both "online live training" and "onsite live training." Online live sessions (also known as "remote live training") are conducted through an interactive remote desktop environment. Onsite live training can be delivered locally at customer premises in Prague or within NobleProg corporate training centers in Prague.
From Prague Main Train Station (Praha hlavní nádraží)
Take tram 9 from Hlavní nádraží toward Sídliště Řepy.
Get off at Újezd.
Walk about 10 minutes toward Malostranské náměstí / Prokopská.
Continue along Prokopská to 296/8.
Alternative: Take the metro C from Hlavní nádraží → Muzeum, change to metro A → Malostranská, then walk across Malá Strana. This involves more walking.
From Prague Bus Station — Florenc
Take metro B from Florenc toward Zličín.
Get off at Můstek.
Change to metro A toward Nemocnice Motol.
Get off at Malostranská.
Walk approximately 10–15 minutes to Prokopská 296/8.
Anchored in the most recent OWASP GenAI Security Project guidance, this session enables participants to detect, evaluate, and counter AI-specific threats through practical exercises and real-world case studies.
This premium, advanced, hands-on workshop engages participants in the essential complexities of contemporary CI/CD pipeline security. Tailored for security specialists, DevOps engineers, and developers seeking to excel in sophisticated pipeline breach mitigation, the course combines live attack simulations with industry-standard tools and actionable defense strategies.
This instructor-led, live training in Prague (available online or on-site) is tailored for web developers and leaders who aim to explore and implement the OWASP Top 10 reference standard to enhance the security of their web applications.
By the end of this course, participants will be equipped to strategize, implement, secure, and monitor web applications and services utilizing the OWASP Top 10 framework.
This instructor-led live training in Prague (online or onsite) targets developers, engineers, and architects who aim to apply the WSTG testing framework, principles, and techniques to secure their web applications and services.
By the end of this training, participants will be able to:
Utilize the WSTG to integrate testing processes and techniques throughout the web development lifecycle.
Examine various testing methodologies to tailor the WSTG framework to specific business requirements.
Execute diverse security testing methods to safeguard web applications against risks and cyberattacks.
Generate assessment reports that thoroughly document security testing findings and outcomes.
This course examines secure coding practices in Java through the lens of the OWASP methodology. Participants will learn to identify web threats, mitigate common attacks such as XSS and CSRF, and apply secure design principles. Join this practical training in Prague to effectively strengthen your application security capabilities.
This instructor-led course in Prague focuses on secure coding concepts and ASP.NET security principles. Participants will learn to apply the OWASP methodology, implement robust authentication and authorization, and mitigate injection attacks, XSS, and CSRF to build resilient, secure web applications.
Read more...
Last Updated:
Testimonials (5)
The training helped me expand my knowledge and understanding of Burp Suite. I also realized that what I had learned through self-study was still quite limited. This training was very helpful to me as a QA because Burp Suite is a valuable tool for performing security testing and improving the overall quality of application testing. I will continue exploring this tool and learning more about its features and capabilities.
Rea Mendez - BAKAWAN Data Anallytics Inc.
Course - OWASP Top 10 2025
I really enjoyed learning about AI attacks and the tools out there to begin practicing and actively using for security testing. I took a lot of knowledge away which I didn't have at the beginning and the course met what I hoped it would be. My favorite part shown from the training was Comet Browser and was amazed at what it could do. Definitely something will be looking into more. Overall it was a great course and enjoyed learning all OWASP GenAI Top 10.
Patrick Collins - Optum
Course - OWASP GenAI Security
The topic is current and I needed to be updated
Damilano Marco - SIAP s.r.l.
Course - Secure Developer Java (Inc OWASP)
Introductions to the many different types of unsafe behaviors.
Online OWASP training in Prague, OWASP training courses in Prague, Weekend OWASP courses in Prague, Evening OWASP training in Prague, OWASP instructor-led in Prague, OWASP on-site in Prague, OWASP one on one training in Prague, OWASP trainer in Prague, Online OWASP training in Prague, OWASP private courses in Prague, Weekend OWASP training in Prague, OWASP coaching in Prague, OWASP classes in Prague, Evening OWASP courses in Prague, OWASP instructor in Prague, OWASP boot camp in Prague, OWASP instructor-led in Prague