Delivered either online or onsite, our instructor-led Threat Detection and Response (TDR) training courses provide an interactive, hands-on approach to mastering advanced techniques and tools. These sessions are designed to enable participants to effectively identify, analyze, and mitigate cybersecurity threats in real-time environments.
Threat Detection and Response training is offered in two formats: "online live training" and "onsite live training". The online option, also known as "remote live training", utilizes an interactive remote desktop environment. Onsite live training can be conducted locally at your customer premises in Prague or within NobleProg corporate training centers in Prague.
From Prague Main Train Station (Praha hlavní nádraží)
Take tram 9 from Hlavní nádraží toward Sídliště Řepy.
Get off at Újezd.
Walk about 10 minutes toward Malostranské náměstí / Prokopská.
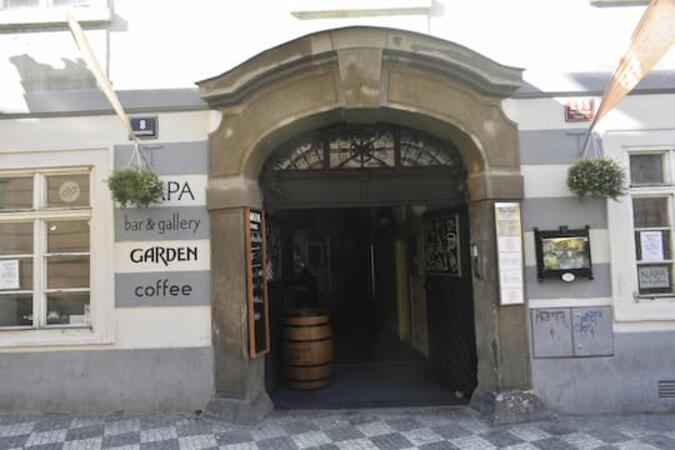
Continue along Prokopská to 296/8.
Alternative: Take the metro C from Hlavní nádraží → Muzeum, change to metro A → Malostranská, then walk across Malá Strana. This involves more walking.
From Prague Bus Station — Florenc
Take metro B from Florenc toward Zličín.
Get off at Můstek.
Change to metro A toward Nemocnice Motol.
Get off at Malostranská.
Walk approximately 10–15 minutes to Prokopská 296/8.
This instructor-led live training, located in Prague (available online or on-site), is targeted at intermediate cybersecurity professionals seeking to implement CTEM within their organizations.
By the end of this training, participants will be able to:
Grasp the core principles and phases of CTEM.
Pinpoint and rank risks by applying CTEM methodologies.
Incorporate CTEM practices into current security frameworks.
Leverage specific tools and technologies for ongoing threat management.
Formulate strategies for the continuous validation and enhancement of security controls.
This instructor-led, live training in Prague (online or onsite) is aimed at intermediate-level cybersecurity professionals who wish to leverage DeepSeek for advanced threat detection and automation.
By the end of this training, participants will be able to:
Utilize DeepSeek AI for real-time threat detection and analysis.
Implement AI-driven anomaly detection techniques.
Automate security monitoring and response using DeepSeek.
Integrate DeepSeek into existing cybersecurity frameworks.
Join this instructor-led training in Prague to master the fundamentals of OpenEDR. You will learn to deploy agents, configure telemetry, and analyze endpoint events for effective threat detection. Hands-on labs in Prague emphasize incident response and the integration of alerts into security workflows.
This advanced training in Prague empowers SOC analysts and threat hunters with practical skills to deploy OpenEDR and align it with MITRE ATT&CK. Participants will acquire the ability to design detection logic, execute hunting workflows, and perform root cause analysis to enhance organizational security posture.
This instructor-led training in Prague empowers security professionals with advanced ransomware negotiation techniques and threat intelligence expertise. Participants will dissect attack lifecycles, engage in simulated negotiations, and leverage intelligence to establish robust defensive postures.
This instructor-led, live training in Prague (online or onsite) is designed for advanced-level cybersecurity professionals who aim to comprehend Cyber Threat Intelligence and develop skills to effectively manage and mitigate cyber threats.
By the end of this training, participants will be able to:
Grasp the fundamentals of Cyber Threat Intelligence (CTI).
Analyze the current cyber threat landscape.
Collect and process intelligence data.
Perform advanced threat analysis.
Leverage Threat Intelligence Platforms (TIPs) and automate threat intelligence processes.
This live, instructor-led training in Prague empowers beginner-level cybersecurity practitioners to master the fundamentals of detection engineering. Learners will gain the skills to craft effective rules, interpret complex logs, utilize threat intelligence, and optimize alert workflows to reduce noise in modern SOC environments.
Instructor-led training in Prague designed for IT security professionals. Master incident planning, classification, containment, and management through hands-on simulations. Strengthen practical skills in detection, eradication, and recovery strategies to enhance your organization's response capabilities.
This advanced training in Prague empowers security researchers with the expertise to automate workflows and expand reconnaissance capabilities for bug bounty hunting. Learners will acquire proficiency in detecting high-impact vulnerabilities, developing custom scripts, and efficiently managing complex targets.
This live, instructor-led training in Prague provides beginners with the essential skills for ethical bug hunting, exploring key tools like Burp Suite and widespread vulnerabilities such as XSS, SQLi, and CSRF. Learners will gain the ability to pinpoint security flaws and produce clear, professional reports.
This instructor-led, live training in Prague (online or onsite) is designed for intermediate-level duty managers and operational leaders who wish to build robust cyber resilience strategies to safeguard their organizations against cyber threats.
By the end of this training, participants will be able to:
Understand cyber resilience fundamentals and their relevance to duty management.
Develop incident response plans to maintain operational continuity.
Identify potential cyber threats and vulnerabilities within their environment.
Implement security protocols to minimize risk exposure.
Coordinate team response during cyber incidents and recovery processes.
This instructor-led, live training in Prague (online or onsite) is designed for intermediate-level IT security professionals who wish to develop skills in security monitoring, analysis, and response.
By the end of this training, participants will be able to:
Comprehend the role of the Blue Team within cybersecurity operations.
Leverage SIEM tools for security monitoring and log analysis.
Detect, analyze, and respond to security incidents effectively.
Conduct network traffic analysis and gather threat intelligence.
Implement best practices in Security Operations Center (SOC) workflows.
This instructor-led, live training in Prague (online or on-site) is designed for intermediate to advanced cybersecurity professionals who wish to enhance their skills in AI-driven threat detection and incident response.
By the end of this training, participants will be able to:
Implement advanced AI algorithms for real-time threat detection.
Customize AI models for specific cybersecurity challenges.
Develop automation workflows for threat response.
Secure AI-driven security tools against adversarial attacks.
This instructor-led, live training in Prague (online or in-person) is designed for entry-level cybersecurity professionals who wish to learn how to leverage AI for improved threat detection and response capabilities.
By the end of this training, participants will be able to:
Understand AI applications in cybersecurity.
Implement AI algorithms for threat detection.
Automate incident response with AI tools.
Integrate AI into existing cybersecurity infrastructure.
This vendor-neutral CHFI training in Prague provides investigators with foundational digital forensics competencies, including evidence collection, chain-of-custody management, and advanced analysis techniques. It prepares professionals to effectively manage digital evidence for legal proceedings and corrective measures through practical, hands-on laboratory exercises.
This instructor-led, live training in Prague (online or on-site) covers various aspects of enterprise security, spanning from AI to database security. It also includes the latest tools, processes, and mindsets required to protect against attacks.
This instructor-led, live training in Prague (online or onsite) is designed for information system analysts who wish to utilize MITRE ATT&CK to mitigate the risk of security compromises.
By the end of this training, participants will be able to:
Set up the required development environment to start implementing MITRE ATT&CK.
Classify the ways attackers interact with systems.
Document adversary behaviors within systems.
Track attacks, decipher patterns, and rate defense tools already in place.
It did give me the insight what I needed :) I am starting teaching on a BTEC Level 3 qualification and wanted to widen my knowledge in this area.
Otilia Pasareti - Merthyr College
Course - Fundamentals of Corporate Cyber Warfare
- Understanding that ATT&CK creates a map that makes it easy to see, where an organization is protected and where the vulnerable areas are. Then to identify the security gaps that are most significant from a risk perspective.
- Learn that each technique comes with a list of mitigations and detections that incident response teams can employ to detect and defend.
- Learn about the various sources and communities for deriving Defensive Recommendations.
Online TDR (Threat Detection and Response) training in Prague, Threat Detection and Response (TDR) training courses in Prague, Weekend Threat Detection and Response courses in Prague, Evening Threat Detection and Response (TDR) training in Prague, TDR instructor-led in Prague, TDR (Threat Detection and Response) boot camp in Prague, TDR trainer in Prague, TDR on-site in Prague, TDR (Threat Detection and Response) instructor-led in Prague, Threat Detection and Response private courses in Prague, Online Threat Detection and Response training in Prague, Weekend TDR training in Prague, TDR (Threat Detection and Response) instructor in Prague, TDR (Threat Detection and Response) coaching in Prague, Threat Detection and Response (TDR) one on one training in Prague, Evening TDR courses in Prague, TDR classes in Prague