Guard your AI systems against modern threats through practical, instructor-guided AI Security training.
These live courses focus on securing machine learning models, mitigating adversarial attacks, and developing trustworthy, robust AI architectures.
You can access this training through online live sessions via remote desktop or in-person live training in Prague, both featuring interactive exercises and real-world scenarios.
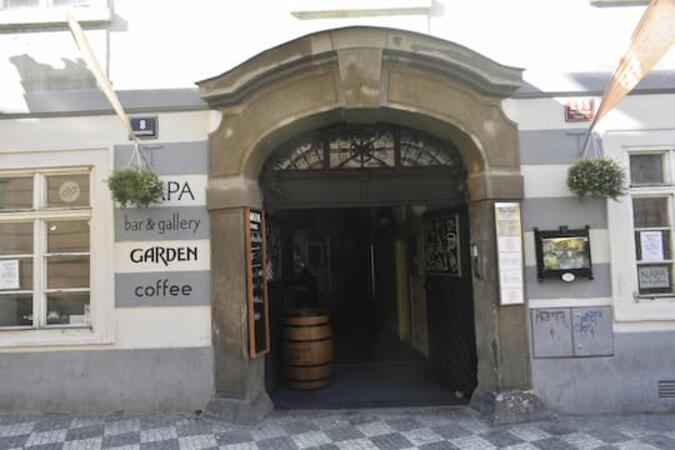
In-person training can be arranged at your facility in Prague or at a NobleProg corporate training center located in Prague.
This discipline is also recognized as Secure AI, ML Security, or Adversarial Machine Learning.
From Prague Main Train Station (Praha hlavní nádraží)
Take tram 9 from Hlavní nádraží toward Sídliště Řepy.
Get off at Újezd.
Walk about 10 minutes toward Malostranské náměstí / Prokopská.
Continue along Prokopská to 296/8.
Alternative: Take the metro C from Hlavní nádraží → Muzeum, change to metro A → Malostranská, then walk across Malá Strana. This involves more walking.
From Prague Bus Station — Florenc
Take metro B from Florenc toward Zličín.
Get off at Můstek.
Change to metro A toward Nemocnice Motol.
Get off at Malostranská.
Walk approximately 10–15 minutes to Prokopská 296/8.
This advanced ISACA course in Prague empowers professionals to effectively govern and secure AI systems. It addresses risk assessment, secure design, and compliance, enabling leaders to align AI security with organizational goals while significantly enhancing operational resilience.
This instructor-led live training in Prague (online or onsite) is designed for IT professionals at beginner to intermediate levels who seek to understand and implement AI TRiSM within their organizations.
Upon completing this training, participants will be equipped to:
Comprehend the fundamental concepts and significance of managing AI trust, risk, and security.
Identify potential risks linked to AI systems and apply mitigation strategies.
Execute security best practices specific to AI environments.
Gain insight into regulatory compliance and ethical implications for AI deployment.
Formulate effective strategies for AI governance and management.
This instructor-led training in Prague focuses on governance, identity management, and red-teaming for agentic AI systems. Advanced practitioners will learn to design secure deployments, implement least-privilege access controls, and perform adversarial testing to mitigate real-world threats in production settings.
This instructor-led, live training in Prague (online or onsite) is aimed at intermediate-level AI and cybersecurity professionals who wish to understand and address the security vulnerabilities specific to AI models and systems, particularly in highly regulated industries such as finance, data governance, and consulting.
By the end of this training, participants will be able to:
Understand the types of adversarial attacks targeting AI systems and methods to defend against them.
Implement model hardening techniques to secure machine learning pipelines.
Ensure data security and integrity in machine learning models.
Navigate regulatory compliance requirements related to AI security.
This instructor-led live training in Prague (online or onsite) is designed for advanced-level security professionals and ML specialists who wish to simulate attacks on AI systems, uncover vulnerabilities, and enhance the robustness of deployed AI models.
By the end of this training, participants will be able to:
Simulate real-world threats to machine learning models.
Generate adversarial examples to test model robustness.
Assess the attack surface of AI APIs and pipelines.
Design red teaming strategies for AI deployment environments.
This guided training session on Prague empowers advanced professionals to secure TinyML pipelines on edge hardware. Learners will acquire the skills to apply privacy-preserving methods, reinforce models against adversarial threats, and adopt best practices for safe data processing in resource-limited contexts.
This instructor-led, live training in Prague (online or onsite) is aimed at intermediate-level engineers and security professionals who wish to secure AI models deployed at the edge against threats such as tampering, data leakage, adversarial inputs, and physical attacks.
By the end of this training, participants will be able to:
Identify and assess security risks in edge AI deployments.
Apply tamper resistance and encrypted inference techniques.
Harden edge-deployed models and secure data pipelines.
Implement threat mitigation strategies specific to embedded and constrained systems.
This instructor-led, live training in Prague (online or onsite) is designed for advanced professionals who wish to implement and evaluate techniques such as federated learning, secure multiparty computation, homomorphic encryption, and differential privacy in real-world machine learning pipelines.
By the end of this training, participants will be able to:
Understand and compare key privacy-preserving techniques in ML.
Implement federated learning systems using open-source frameworks.
Apply differential privacy for safe data sharing and model training.
Use encryption and secure computation techniques to protect model inputs and outputs.
This instructor-led training in Prague empowers public sector IT professionals to master AI risk management and security. Participants will learn to apply frameworks like the NIST AI RMF, mitigate cybersecurity threats, and establish robust governance plans for secure AI deployment.
This instructor-led live training in Prague (online or onsite) is designed for intermediate-level enterprise leaders who wish to learn how to govern and secure AI systems responsibly and in alignment with emerging global frameworks like the EU AI Act, GDPR, ISO/IEC 42001, and the U.S. Executive Order on AI.
By the end of this training, participants will be able to:
Understand the legal, ethical, and regulatory risks of using AI across departments.
Interpret and apply major AI governance frameworks (EU AI Act, NIST AI RMF, ISO/IEC 42001).
Establish security, auditing, and oversight policies for AI deployment in the enterprise.
Develop procurement and usage guidelines for third-party and in-house AI systems.
This instructor-led live training in Prague (online or on-site) is designed for intermediate to advanced AI developers, architects, and product managers seeking to identify and mitigate risks in LLM-powered applications. Key risk areas include prompt injection, data leakage, and unfiltered outputs, with a focus on implementing security controls such as input validation, human oversight, and output guardrails.
By the end of this training, participants will be able to:
Understand the core vulnerabilities of LLM-based systems.
Apply secure design principles to LLM app architecture.
Use tools such as Guardrails AI and LangChain for validation, filtering, and safety.
Integrate techniques like sandboxing, red teaming, and human-in-the-loop review into production-grade pipelines.
This instructor-led, live training in Prague (online or onsite) is designed for intermediate-level professionals in machine learning and cybersecurity who want to understand and mitigate emerging threats against AI models, using both conceptual frameworks and practical defenses like robust training and differential privacy.
By the end of this training, participants will be able to:
Identify and categorize AI-specific threats such as adversarial attacks, inversion, and poisoning.
Utilize tools like the Adversarial Robustness Toolbox (ART) to simulate attacks and evaluate models.
Implement practical defenses, including adversarial training, noise injection, and privacy-preserving techniques.
Design threat-aware model evaluation strategies for production environments.
This instructor-led, live training in Prague (online or onsite) is aimed at beginner-level IT security, risk, and compliance professionals who wish to understand foundational AI security concepts, threat vectors, and global frameworks such as NIST AI RMF and ISO/IEC 42001.
By the end of this training, participants will be able to:
Understand the unique security risks introduced by AI systems.
Identify threat vectors such as adversarial attacks, data poisoning, and model inversion.
Apply foundational governance models like the NIST AI Risk Management Framework.
Align AI use with emerging standards, compliance guidelines, and ethical principles.
Guided by the latest OWASP GenAI Security Project recommendations, participants will learn to identify, assess, and mitigate AI-specific threats through hands-on exercises and real-world scenarios.
This course offers a practical introduction to securing modern AI-powered applications, APIs, copilots, and autonomous agents. Participants will learn how AI security diverges from traditional web security, explore common AI-specific threats such as prompt injection, RAG poisoning, and agent abuse, and understand how to protect AI systems using layered defenses including WAFs, AI gateways, API security measures, and guardrails. Through hands-on labs and real-world examples, students will gain the skills to identify AI attack patterns, secure LLM-based applications, and deploy effective runtime defenses for production environments.
This course teaches software developers how to build AI-powered applications securely by design. Participants learn how to protect chatbots, copilots, RAG pipelines, and AI agents against AI-specific threats such as prompt injection, data poisoning, tool abuse, secret leakage, and insecure model output. The course covers secure prompt design, RAG security, least-privilege access, guardrails, and red-team testing, helping developers build AI features that are secure, reliable, and resilient in real-world environments.
This instructor-led live training in Prague (online or onsite) is aimed at security engineers and compliance officers who wish to harden EXO deployments, control model access, and govern AI workloads running entirely on-premise.
This instructor-led, live training in Prague (online or onsite) is aimed at security and ML engineers who need to identify, test, and defend against attacks on ML models and LLM-powered applications.
Read more...
Last Updated:
Testimonials (3)
inventory and identifying the different risk exposures within AI
Gary Cook - Cybersecurity and Information Technology Risk Division
Course - Introduction to AI Trust, Risk, and Security Management (AI TRiSM)
I really enjoyed learning about AI attacks and the tools out there to begin practicing and actively using for security testing. I took a lot of knowledge away which I didn't have at the beginning and the course met what I hoped it would be. My favorite part shown from the training was Comet Browser and was amazed at what it could do. Definitely something will be looking into more. Overall it was a great course and enjoyed learning all OWASP GenAI Top 10.
Patrick Collins - Optum
Course - OWASP GenAI Security
The profesional knolage and the way how he presented it before us
Online Secure AI training in Prague, AI Security training courses in Prague, Weekend AI Security courses in Prague, Evening AI Security training in Prague, Secure AI instructor-led in Prague, Secure AI coaching in Prague, Secure AI trainer in Prague, Secure AI on-site in Prague, Secure AI instructor in Prague, Secure AI classes in Prague, Online AI Security training in Prague, AI Security one on one training in Prague, Secure AI boot camp in Prague, Secure AI instructor-led in Prague, AI Security private courses in Prague, Evening Secure AI courses in Prague, Weekend Secure AI training in Prague